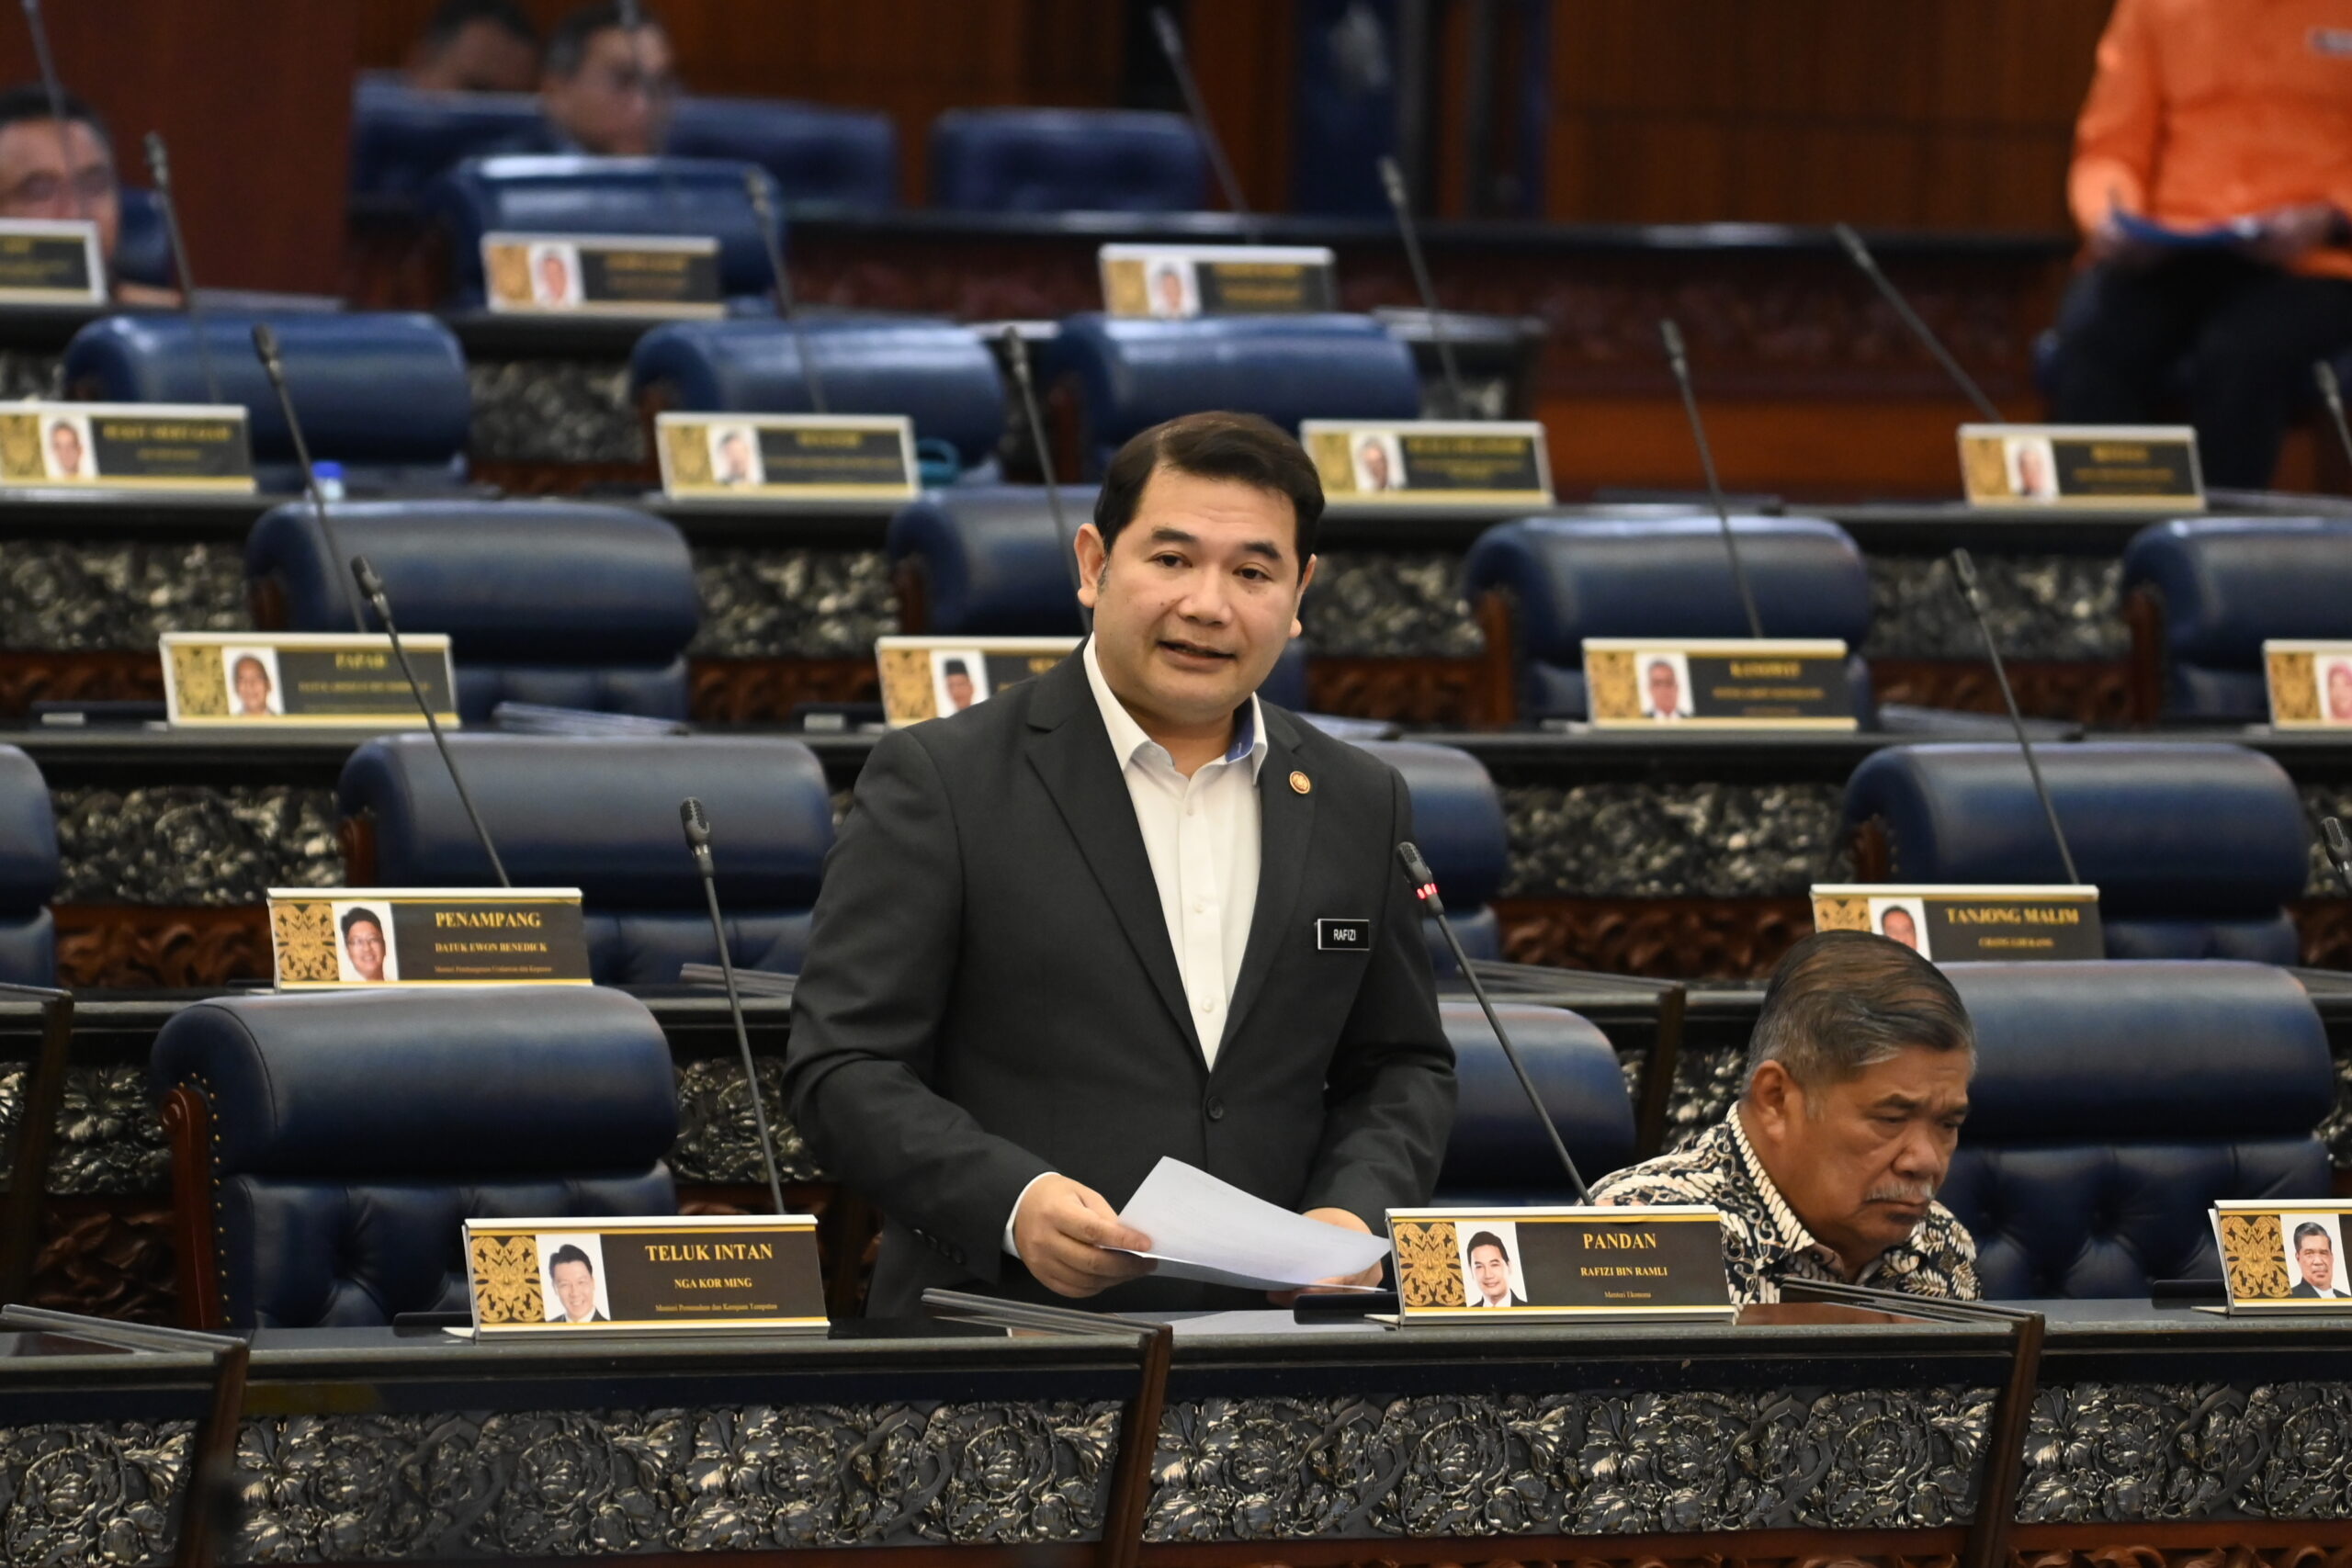
KUALA LUMPUR – The government’s Central Database Hub (Padu) remains safe and unaffected by the millions of digital attacks on it since its launch, Economy Minister Rafizi Ramli said.
Rafizi (Pandan-PH) told the Dewan Rakyat today that Padu has faced an average of about 2 million to 2.3 million digital attacks every week since it was launched on February 2.
However, quick reactions from the civil servants managing the database have ensured the system’s safety.
“Padu recorded 28 DDoS (distributed denial of service) attacks on February 2 and 3. As of February 4 until now, there have been no more DDoS attacks.
“Our IPS (intrusion prevention system) recorded 32.86 million attacks from February 3 to March 4, all of which were successfully blocked, while a total of 3 million firewall blocks have been implemented since February 2,” he said when winding up MPs’ debates on the royal address.
Rafizi also said that the Padu team’s decision to establish geofencing measures, which prohibit those outside of Malaysia from accessing the database, is to ensure the system’s security.
“Overall, as of now, Padu’s safety system is sufficient and firm. This is thanks to the Padu development team, which is constantly monitoring (the system) and on the watchout for attacks (by) working 18 to 20 hours a day, seven days a week,” he added.
Last month, hacker group R00TK1T’s claims to have hacked into Padu were proven to be false, with the National Population and Family Development Board clarifying that the hack was instead on its unit with the same acronym.
Rafizi had also taken to social media to deny reports that Padu’s security had been breached.
The minister also stood firm on his decision to appoint civil officers to the team behind Padu’s development without the involvement of any third-party, asserting that this saved taxpayers’ money while enhancing the expertise of government staff.
“Certain quarters outside the Dewan insist on raising the issue of data leaks (on Padu), but this makes me uncomfortable sometimes. It’s as if they’re belittling the abilities of our public servants to develop a system like Padu.
“We have proof that even if a system is developed by a third-party with a contract worth a million ringgit, its safety is not guaranteed,” he said, referring to the Covid-19 tracking app MySejahtera, which was developed by a third-party company on a contract basis with the government.
The Auditor-General’s Report 2021 had previously found that an account with full access to MySejahtera’s security settings and administrative features had downloaded data on three million vaccine recipients over the span of three days.
The report stated that the account, a “Super Admin” approved by the Health Ministry, downloaded the information with the help of multiple internet protocol addresses. – March 11, 2024